
Configuring SSO
FOR SPYCLOUD CONSOLE
🧭 Overview
SpyCloud supports Single Sign-On (SSO) through your preferred Identity Provider (IdP), letting users securely log in with existing credentials.
We support Okta, Entra ID (Azure AD), ADFS, and any custom SAML or OIDC provider. SpyCloud’s console, access to user, organization, and license settings is controlled through two built-in roles you can assign to each member of your security team.
🕒 Setup time: ~10 minutes
👤 Required role: Administrator
👇CONFIGURE SSO

🧰 Before You Begin
| Requirement | Description |
|---|---|
| Admin Access | You must have administrator privileges in your SpyCloud Console. |
| IdP Access | Access to Okta, Entra ID, ADFS, or another SAML/OIDC provider. |
| Verified Domains | (Optional) Associate your company email domains with SSO. |
Important:
If you already have 2FA enabled, it will be disabled once SSO is connected.
Your IdP will take over authentication settings, including 2FA, SMS, and password policies.
🚀 Step-by-Step Setup
- Log in to your Console as an Admin.
- Navigate to Configuration → Settings → Security Settings.
- Click Connect Single Sign-On.
- Follow the guided pop-up to complete setup.
👇SECURITY SETTINGS

🧩 Choose Your Identity Provider
| Provider |
|---|
| Okta |
| Entra ID (Azure AD) |
| ADFS |
| Custom SAML or OIDC Provider |
👇EXAMPLE CONFIGURATION FOR OKTA

🔗 Configure in Your IdP
- Add SpyCloud as a new application in your IdP.
- Copy the configuration values shown in SpyCloud:
- Redirect URLs
- Client IDs
- Etc
- Paste these values into your IdP SSO setup form to establish the connection.
💡 Tip: SpyCloud’s SSO workflow is powered by Auth0.
Refer to Auth0 documentation for advanced installation and configuration options.
👇EXAMPLE CONFIGURATION FOR OKTA

☑️ Test Connection
- Click Test Connection to validate setup.
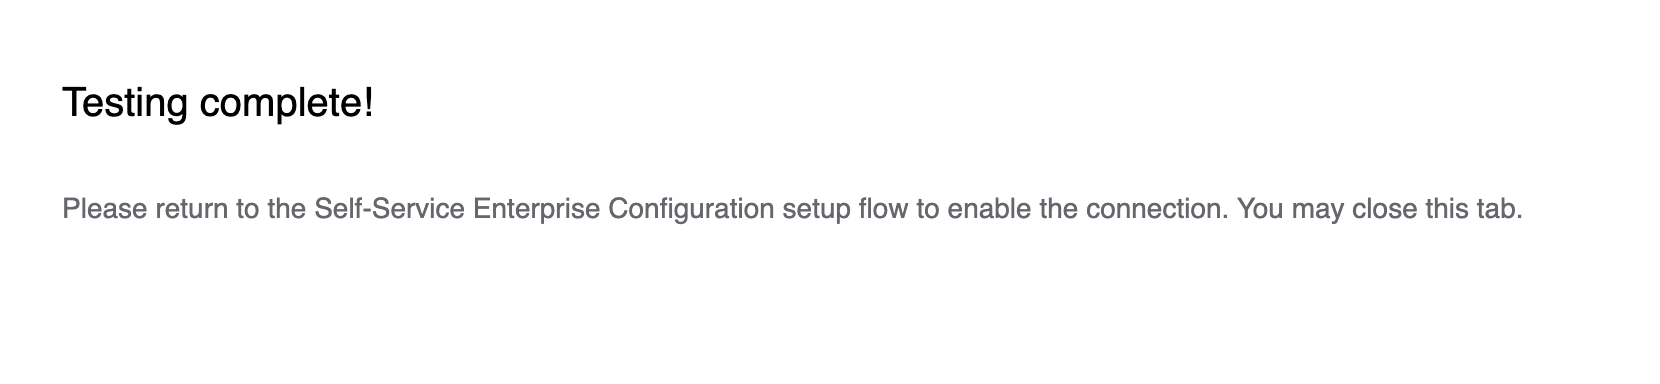
- Close of out the new tab that says "Testing Complete!" and navigate back to the SSO configuration.
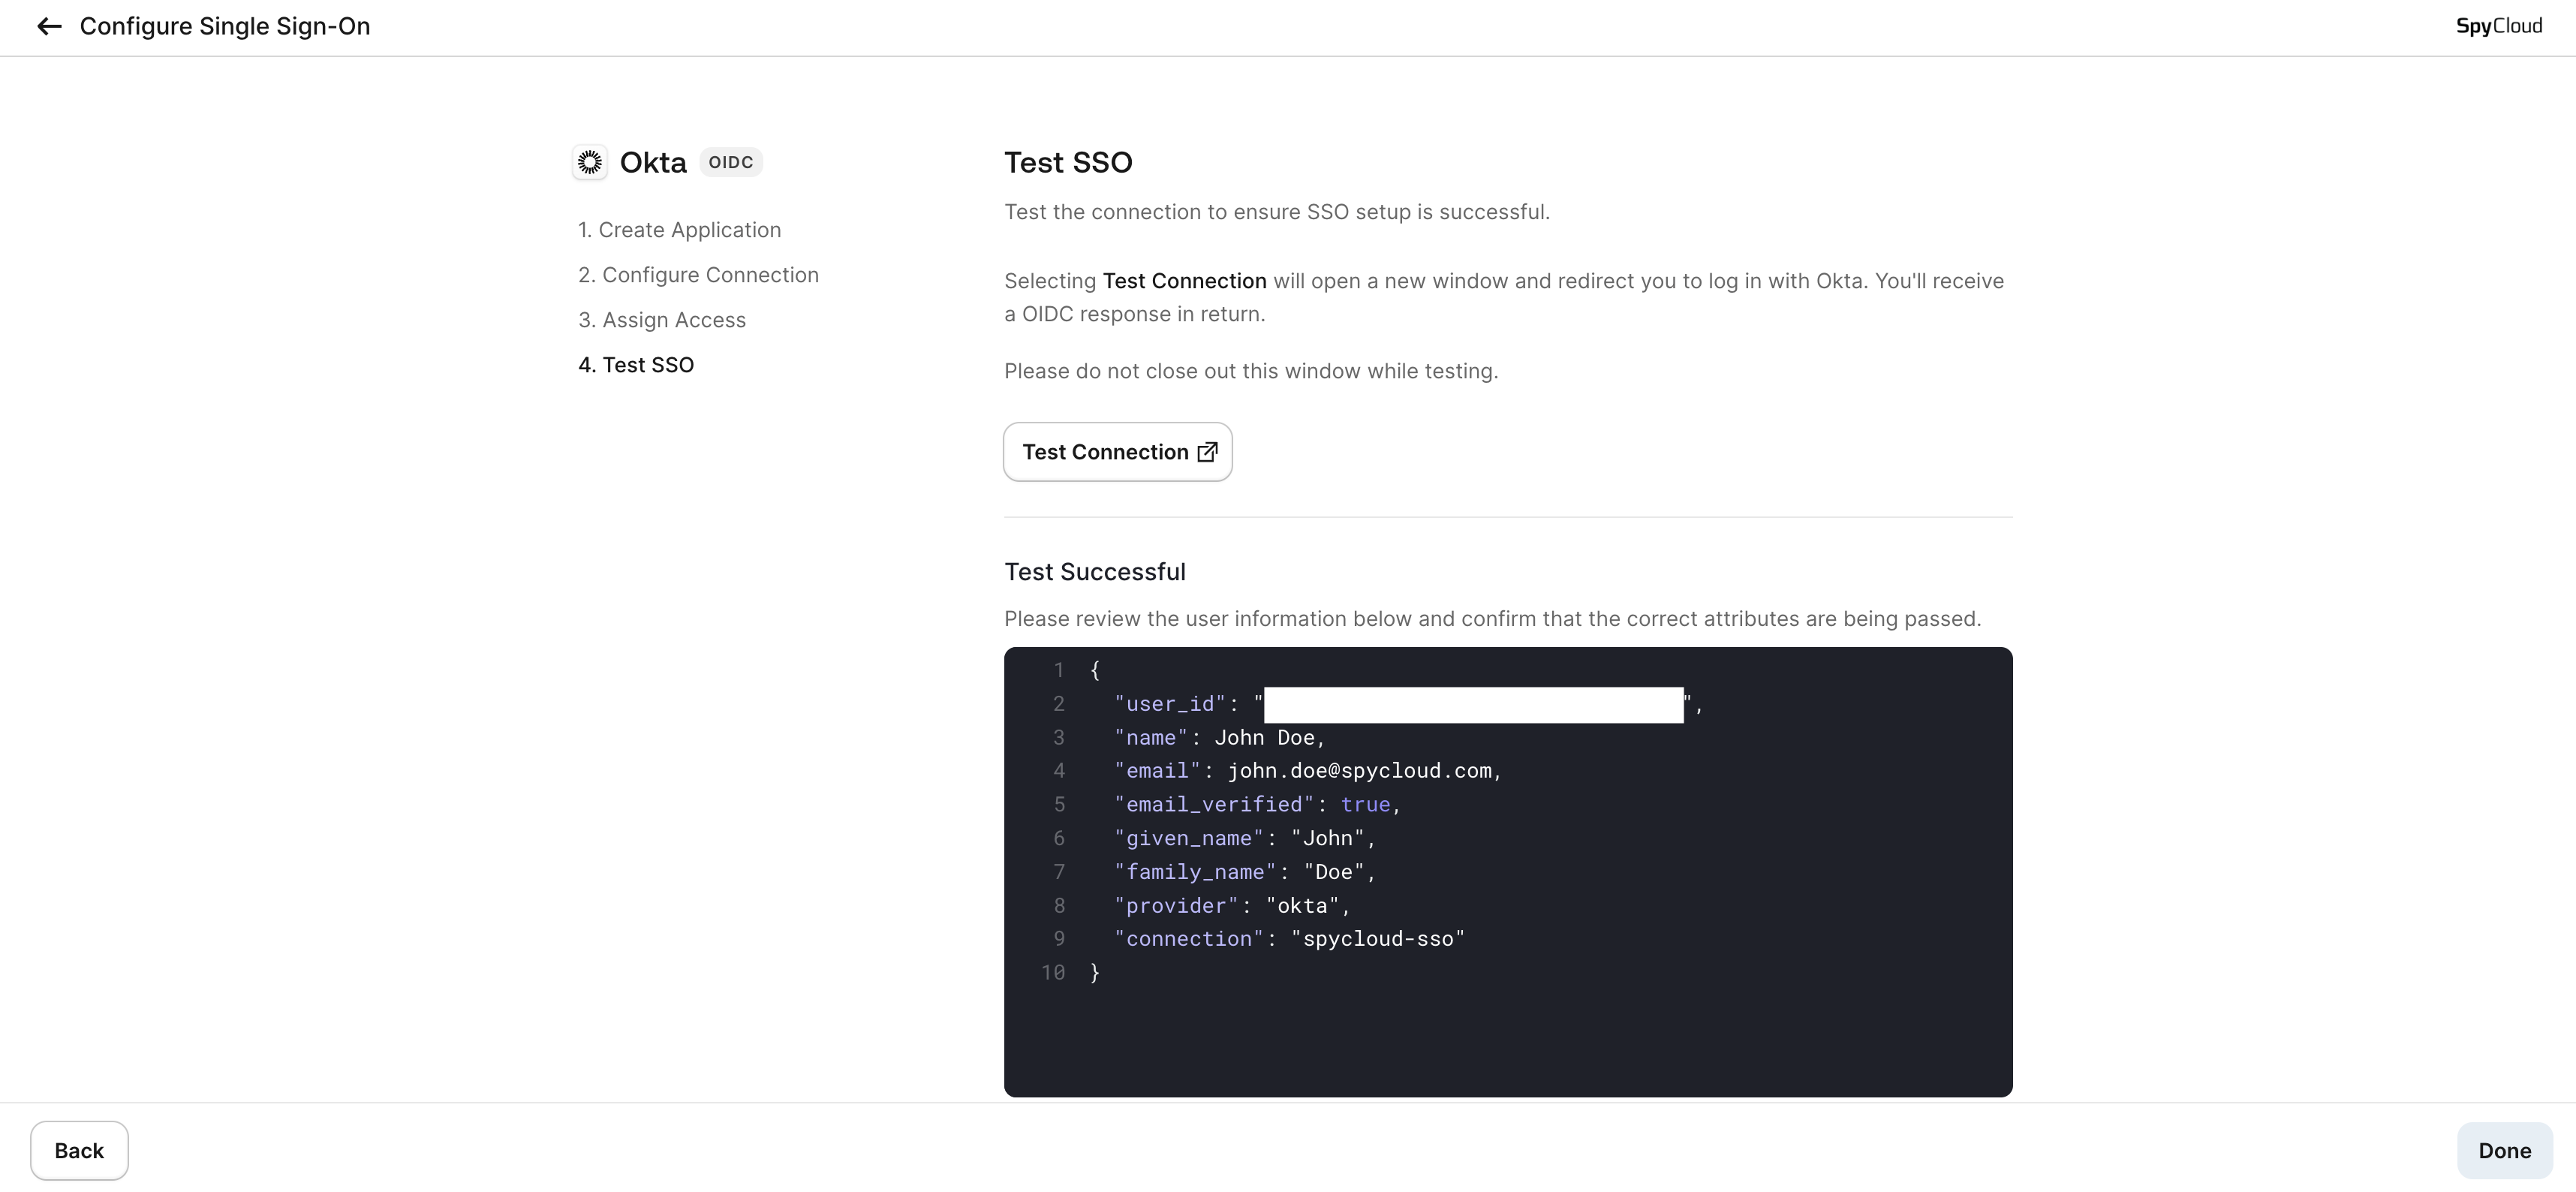
- Review and confirm the user attributes returned in code field.
- Click Done.
👇"TESTING COMPLETE" SECONDARY TAB
👇SUCCESSFUL TEST USER ATTRIBUTES
☑️ Verify Your Domains
All domains require ownership verification for login redirection to work properly. However, the verification process is slightly different depending on the specific domain and selections made earlier in the SSO configuration process.
Primary DomainsSpyCloud associates and verifies a primary domain for every Console organization (e.g. Example Corporation = example.com). This domain may differ from the actual email domains associated with organization users.
Auto Verification
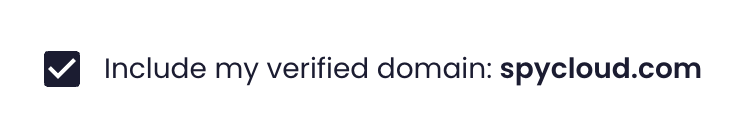
Checking the "Include my verified domain" checkbox in the beginning of the SSO setup flow will auto verify the primary domain associated with the Console organization. No further domain verification is required for the primary domain with this selection.
👇PRIMARY DOMAIN AUTO VERITIFCATION CHECKBOX
Manual Verification
Every other scenario or domain will require manual verification.
- Click on Domain Configuration.
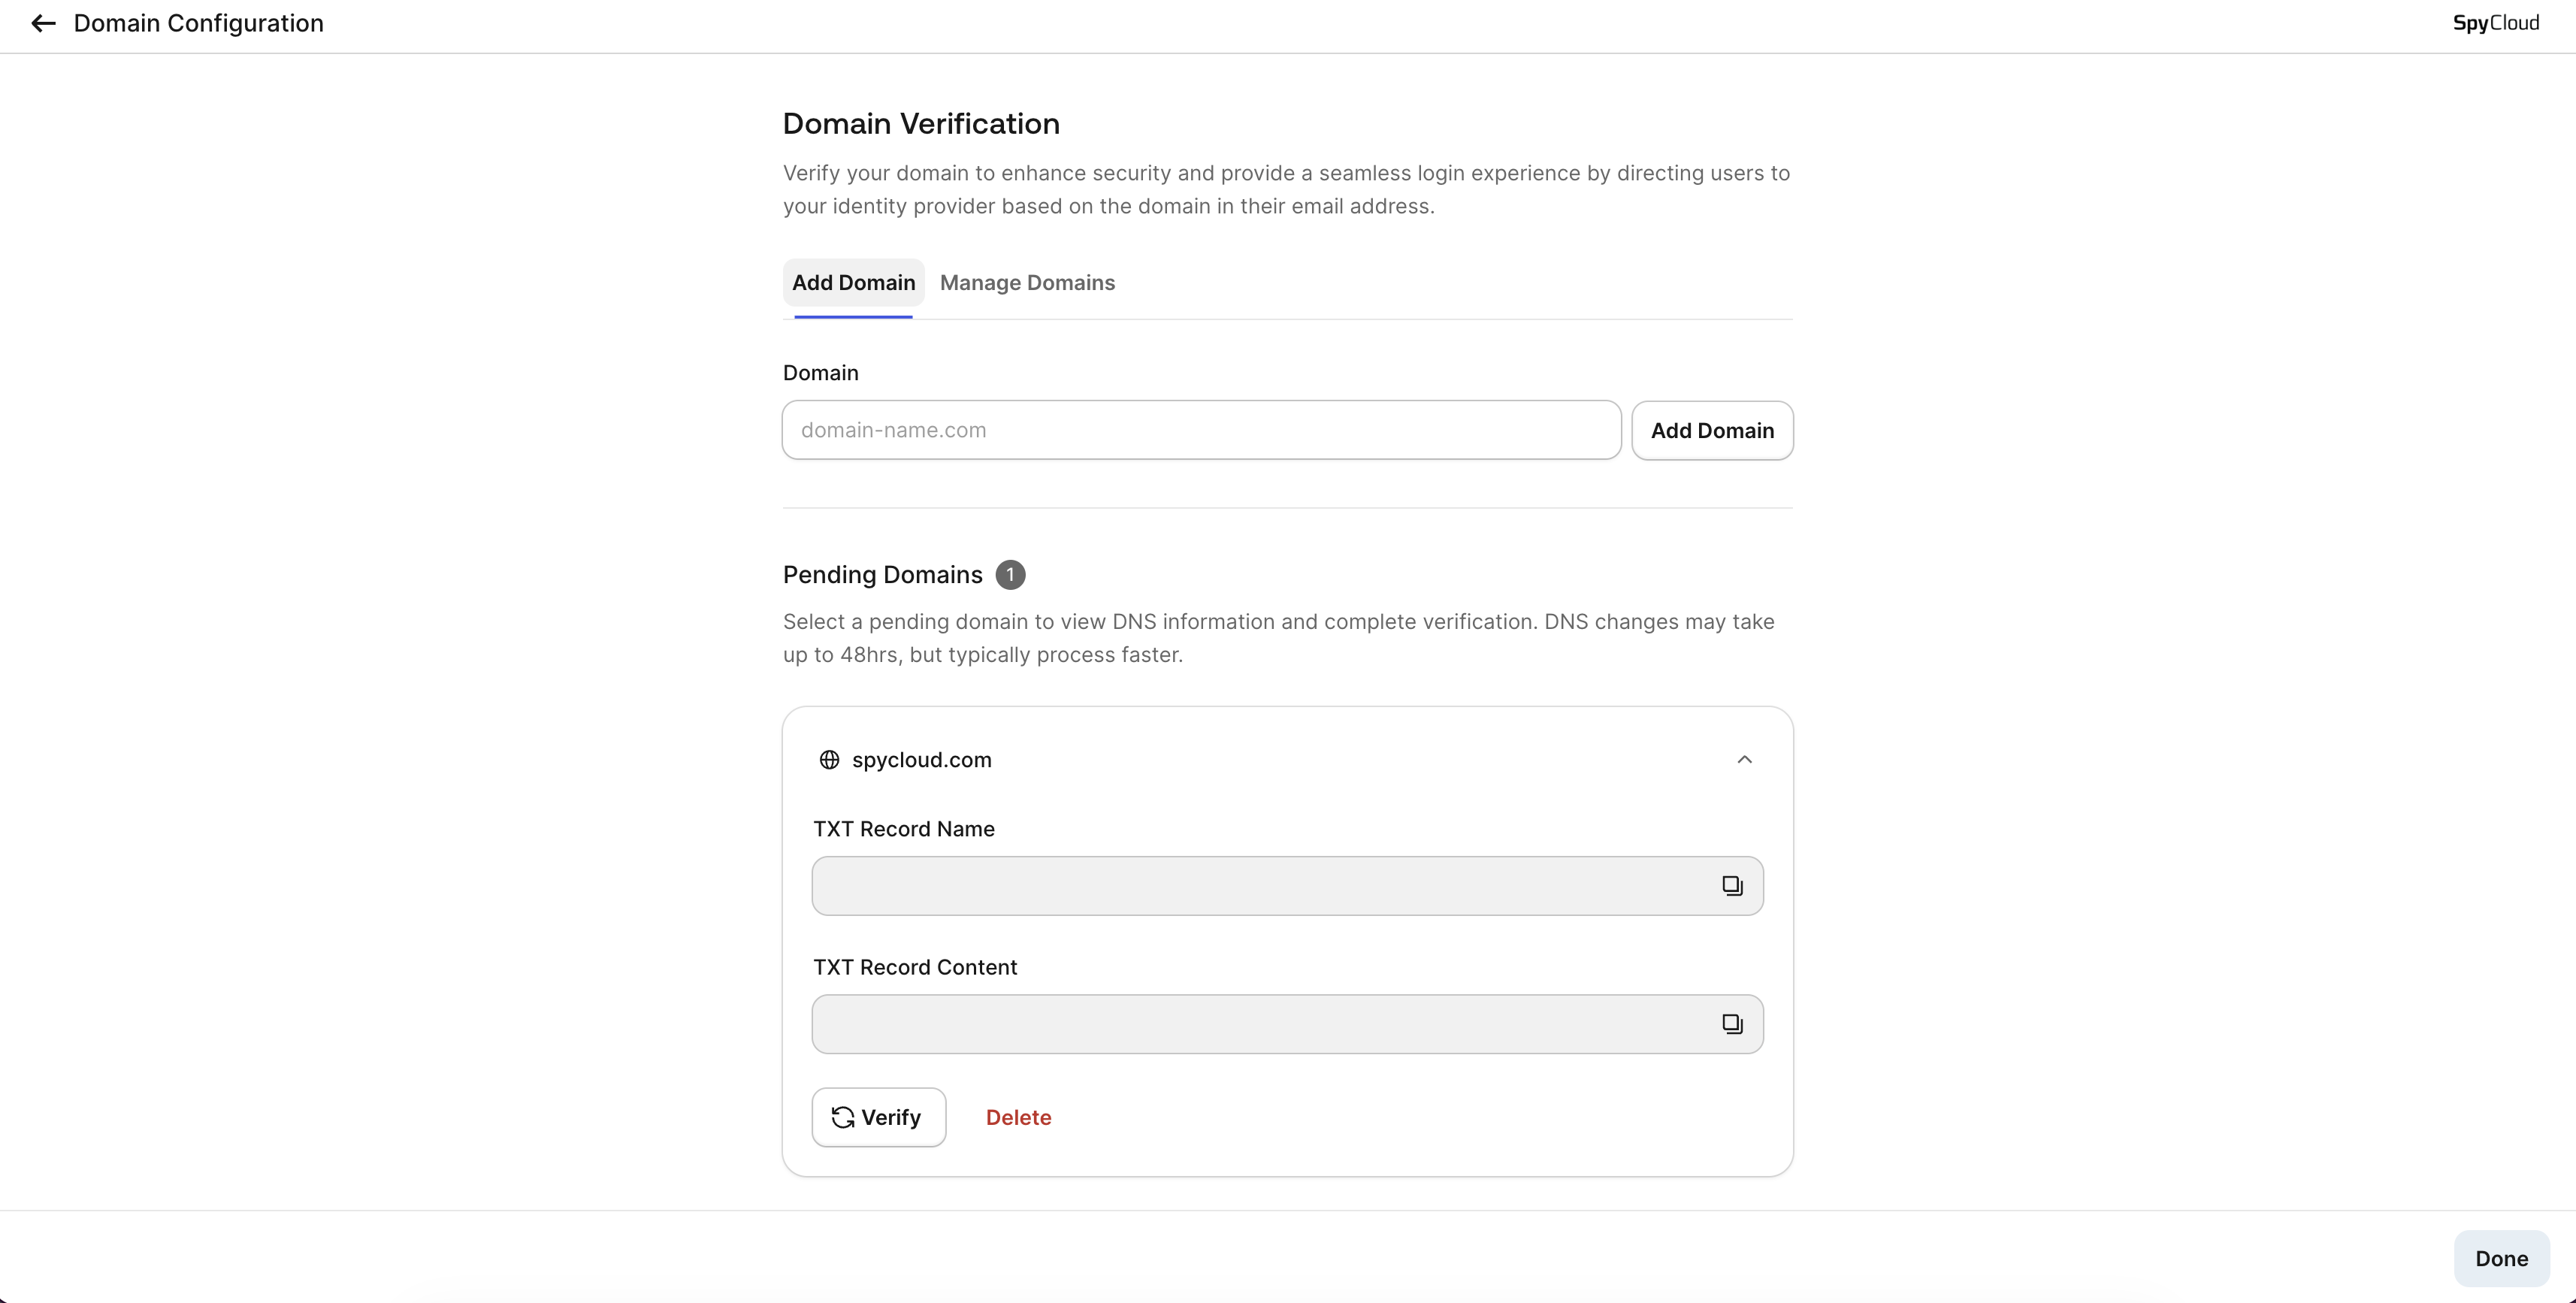
- Select the Add Domain tab and add a domain.
- Create a DNS TXT record with the Name and Content values listed for the domain.
- Click the Verify button once the TXT record has propagated.
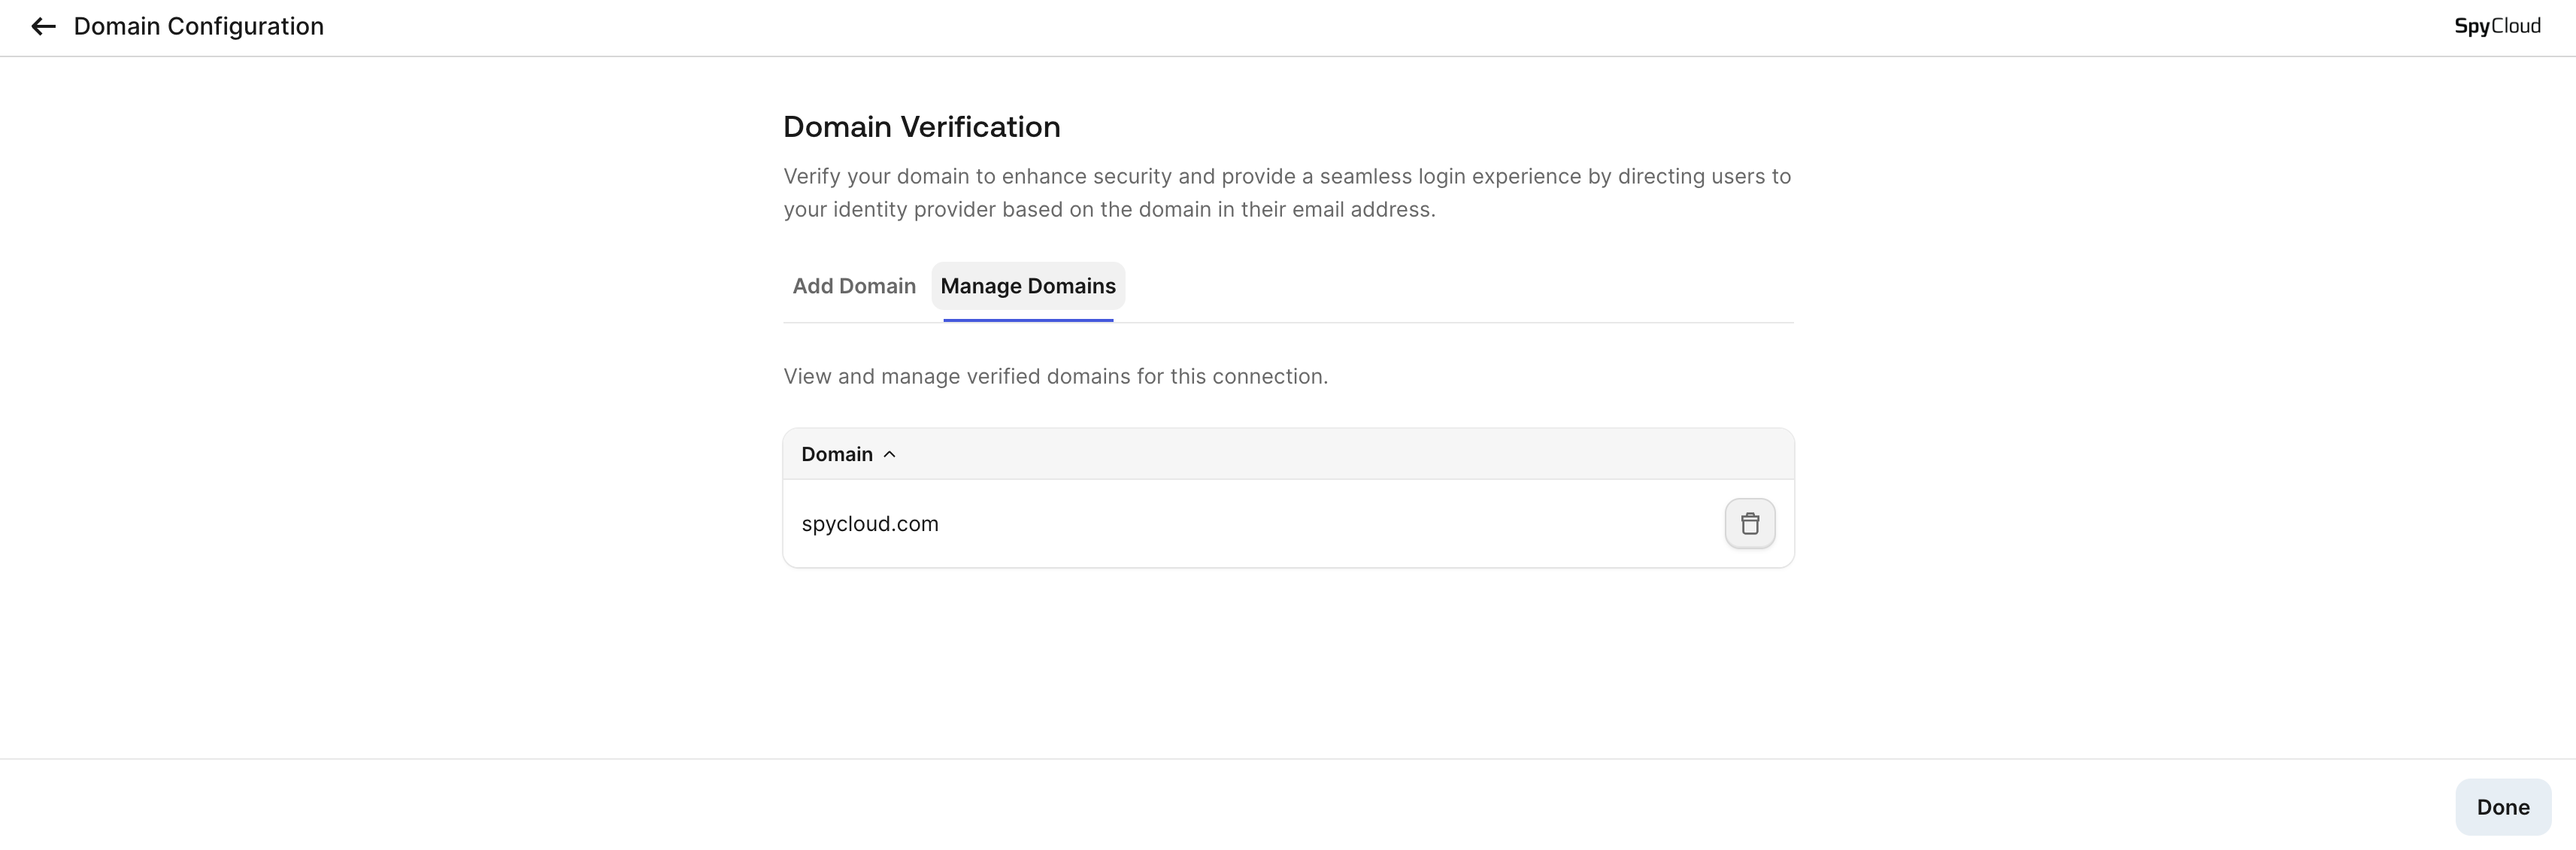
- Confirm the domain is listed under the Managed Domains tab.
👇PENDING DOMAIN TXT RECORD DETAILS
👇MANAGED DOMAINS TAB
✅ Complete SSO Configuration
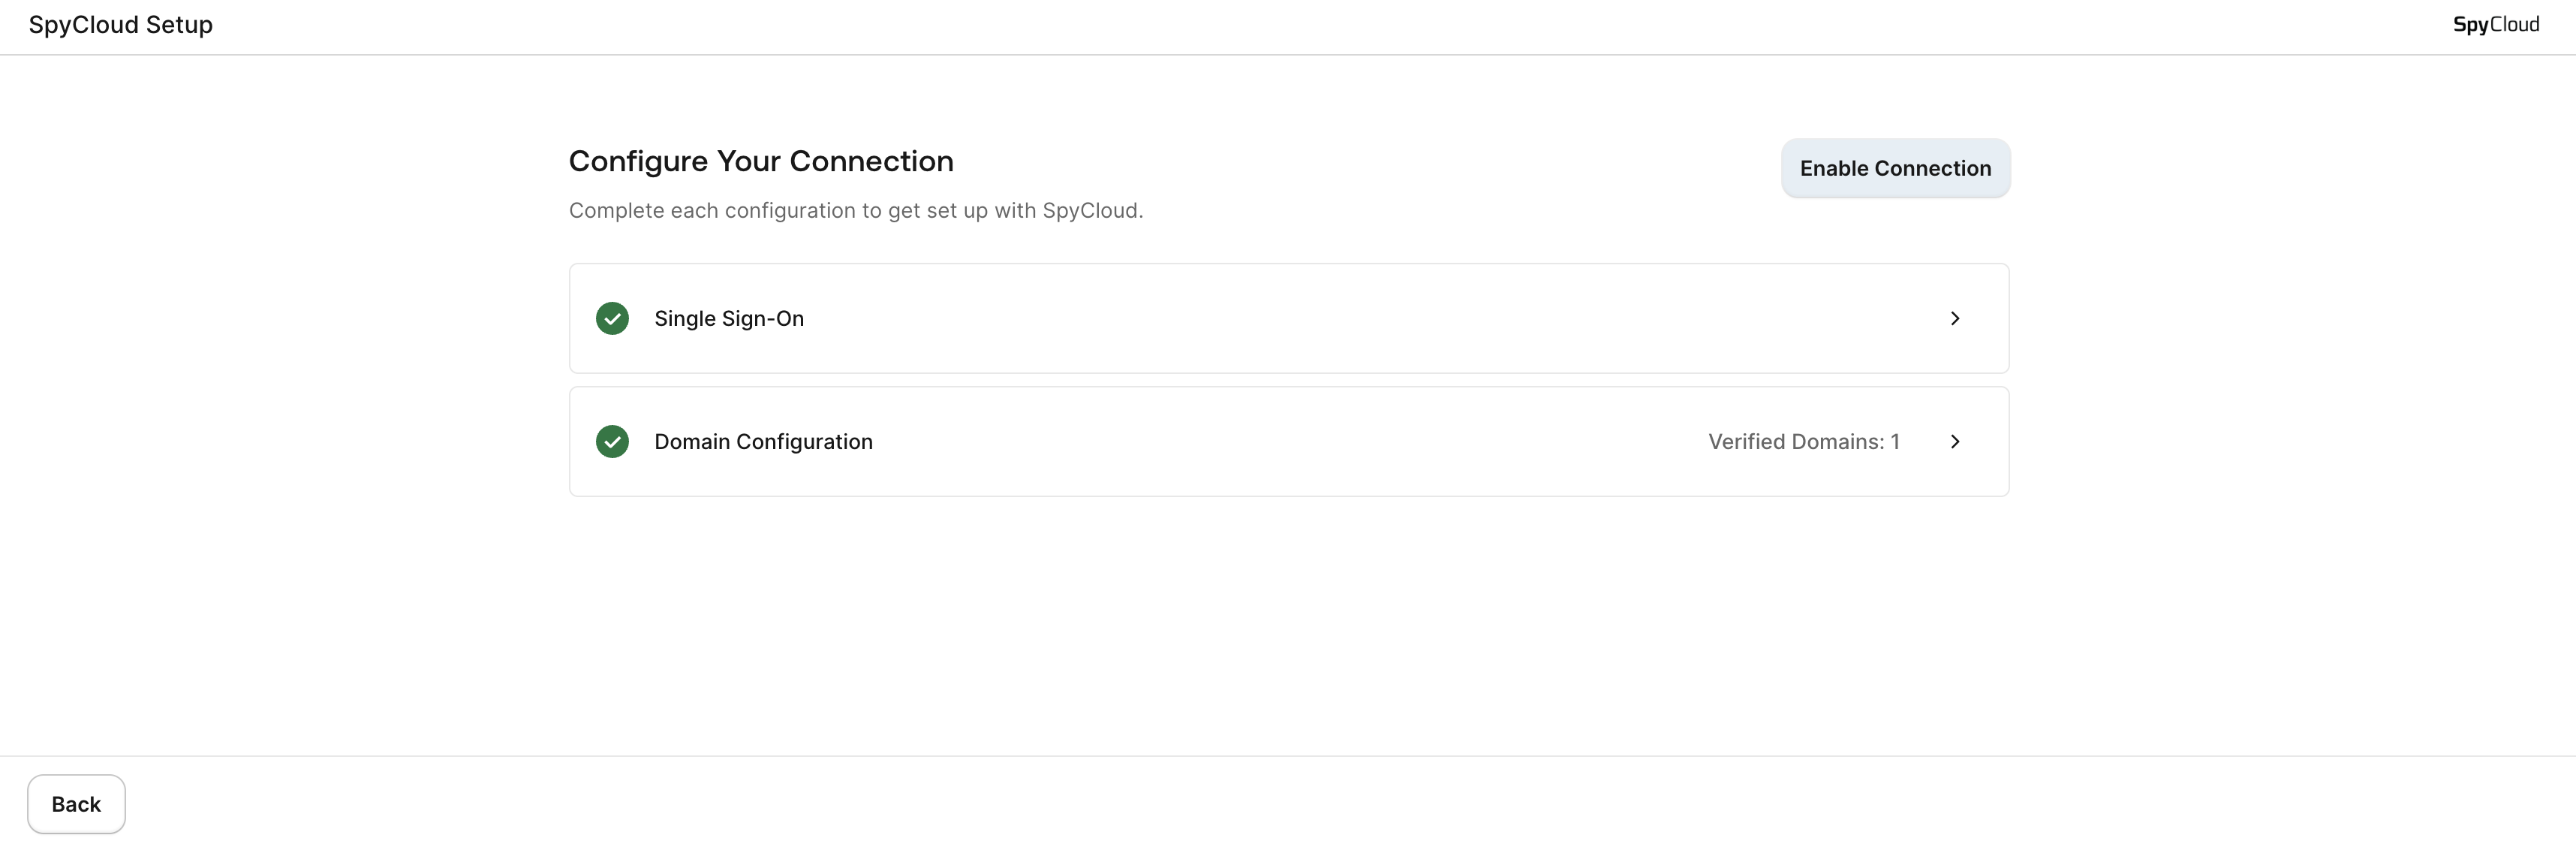
- Ensure both Single Sign-On and Domain Configuration are displaying green checkmarks.
- Confirm the Domain Configuration row lists the correct number of verified domains.
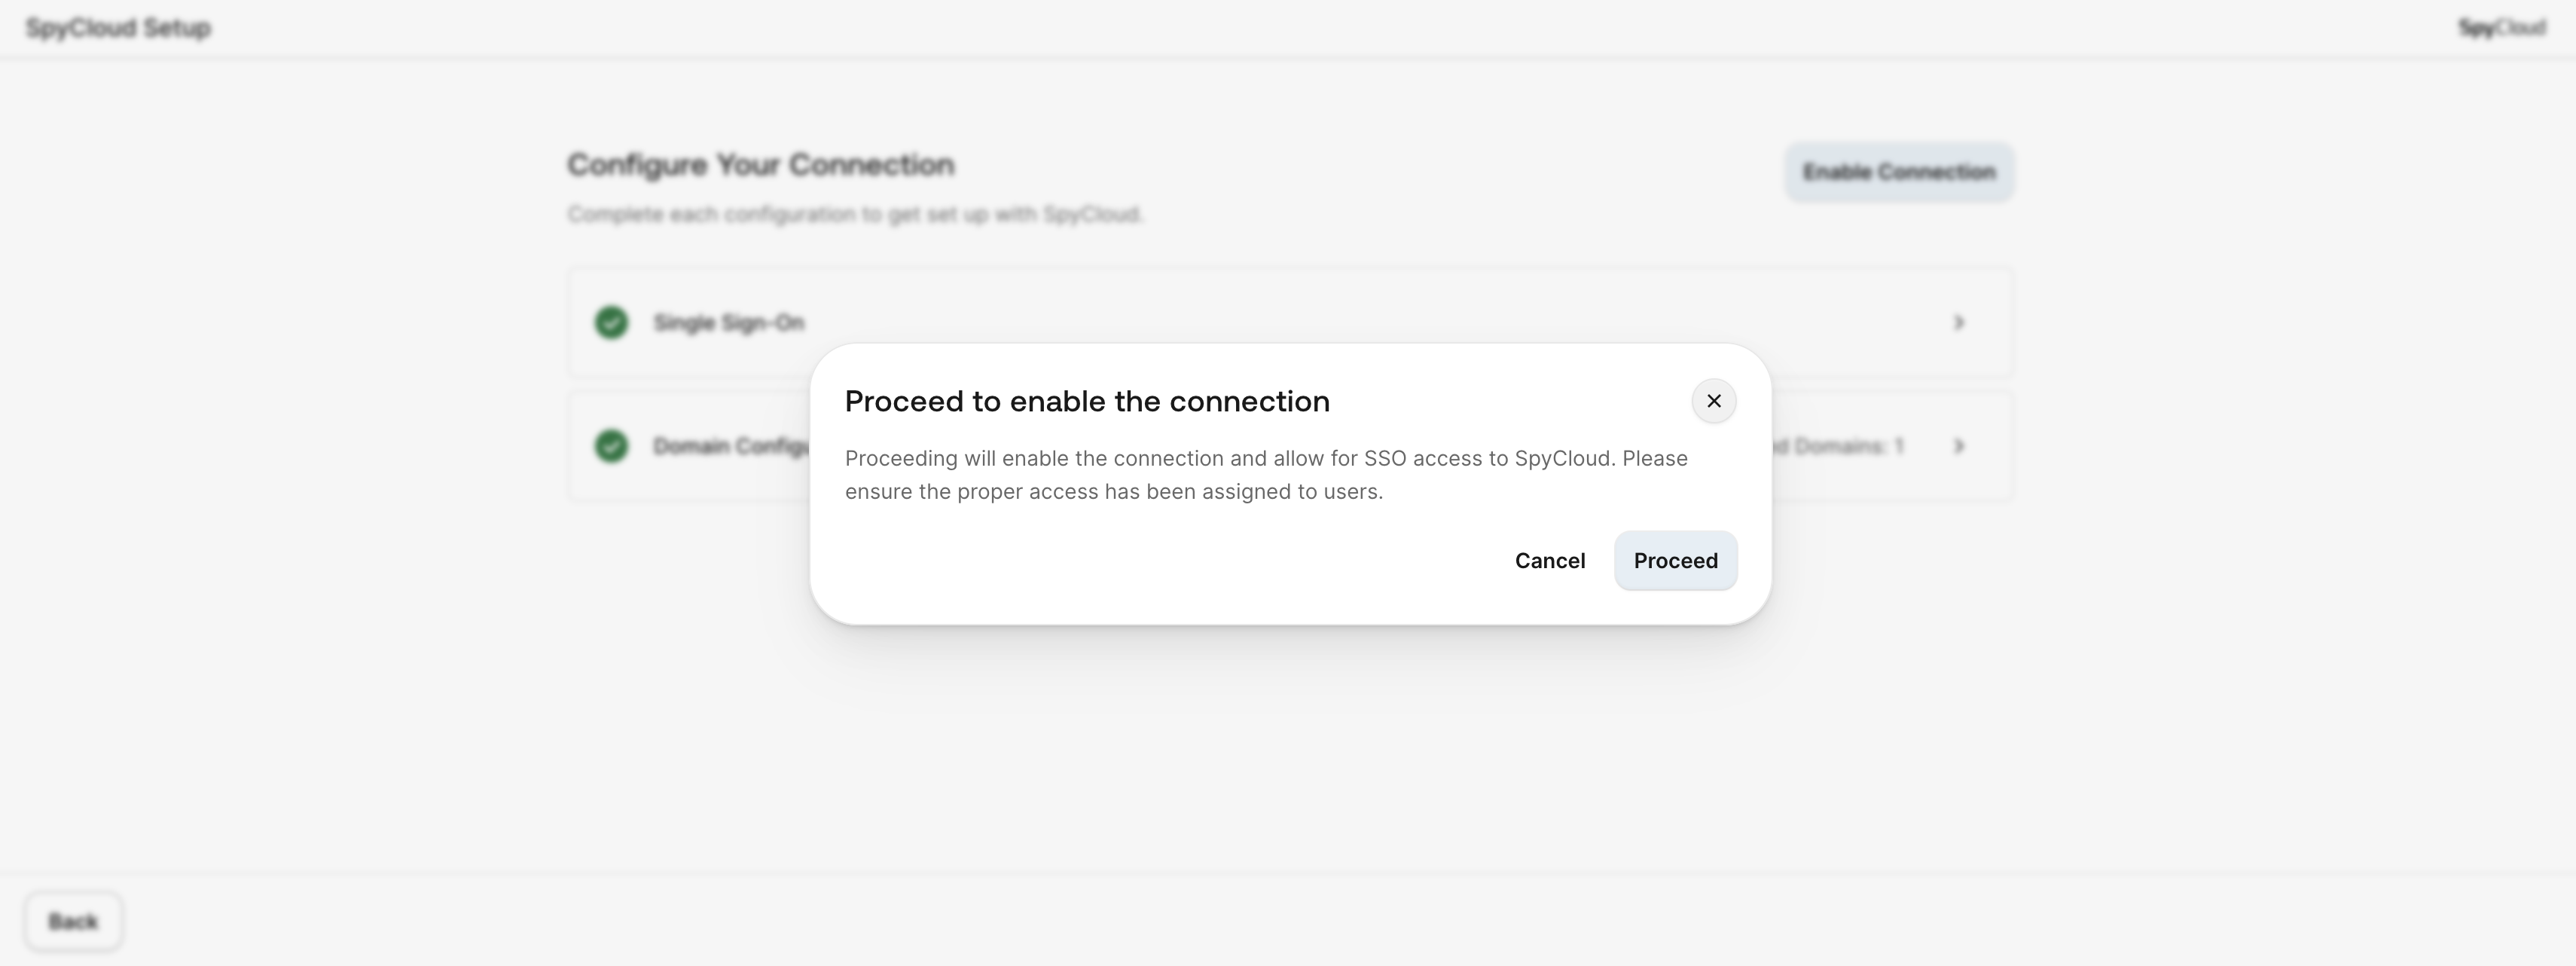
- Click the Enable Connection button.
- Click Proceed on the pop-up window.
👇CONFIGURATION STATUS
👇SSO COMPLETION STEP
🧠 Post-Deployment Expectations
-
IdP manages all authentication (2FA, password policies).
-
Users will sign in via SSO on next login.
-
Admins can update IdP or domains anytime under Configuration → Settings → Security Settings.
🛑 Limitations
- IdP-initiated SSO from a tile is not currently supported.
- SCIM capabilities are currently limited to user provisioning.
Updated 14 days ago